In this post, I’ll walk you through a short but insightful TryHackMe challenge involving a simulated bank platform called FakeBank. This room is great for practicing web enumeration using tools like Gobuster, and also introduces basic privilege abuse on a fake bank transfer system. Let's dive into the methodology and what we discovered.
Step-by-step Guide:
1. Initial Reconnaissance
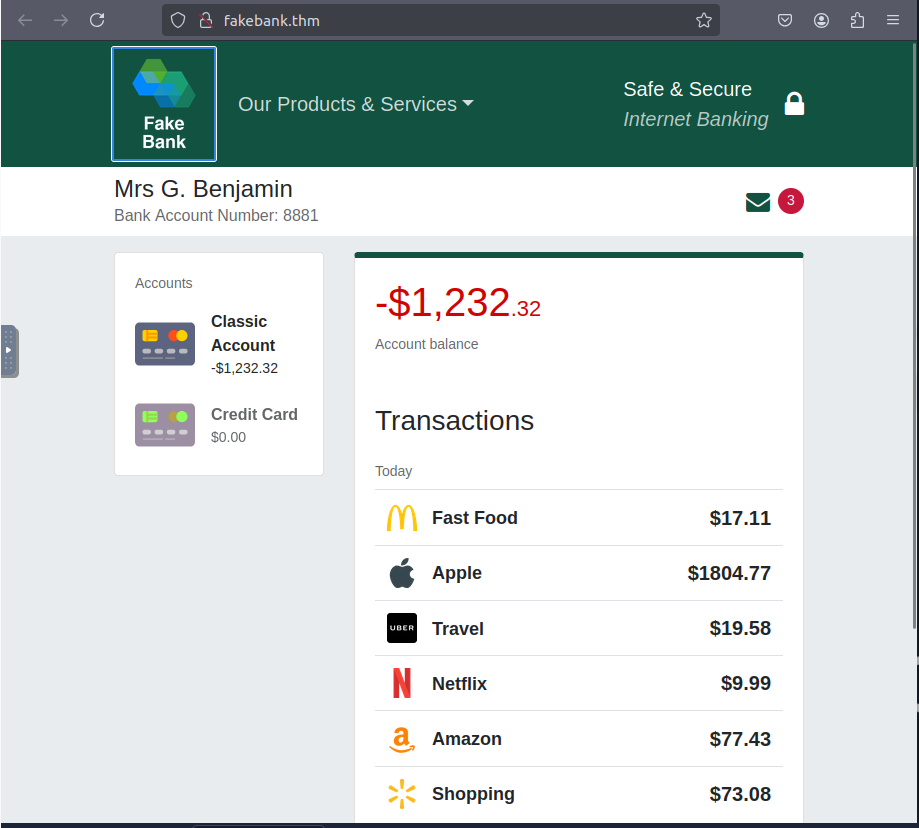
Once inside the room, we’re directed to a target domain:http://fakebank.thm
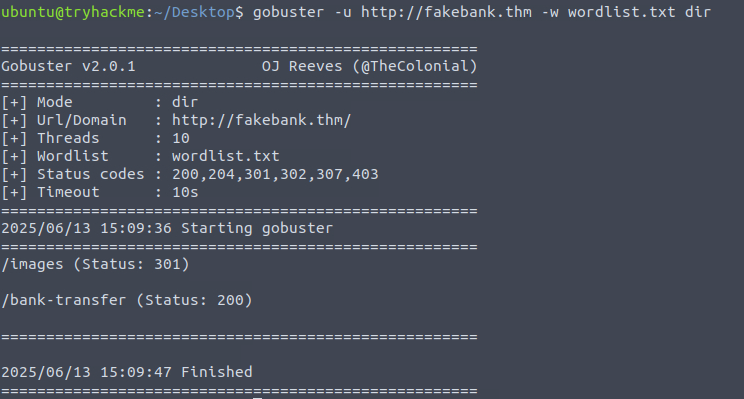
TryHackMe recommends starting with Gobuster to enumerate directories. The command used was:
gobuster dir -u http://fakebank.thm -w wordlist.txt
Discovering Hidden Endpoints
Gobuster reveals two directories:
/image/bank-transfer
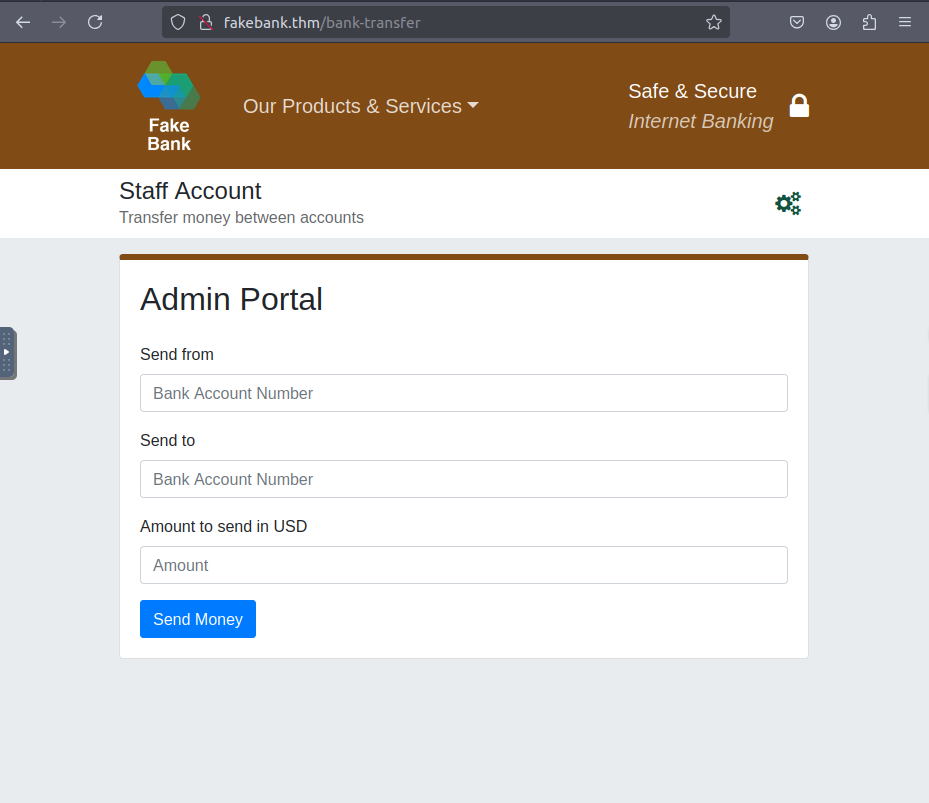
The second one is particularly interesting. When accessed, it redirects to a bank transfer interface.
Exploiting the Transfer Form
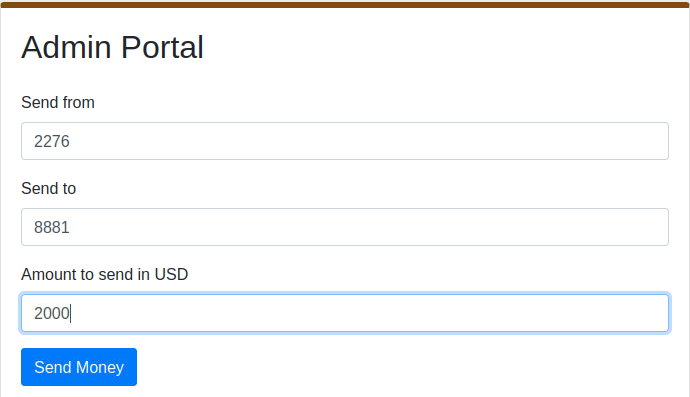
Here, we are able to initiate a transaction from another user account to our own.
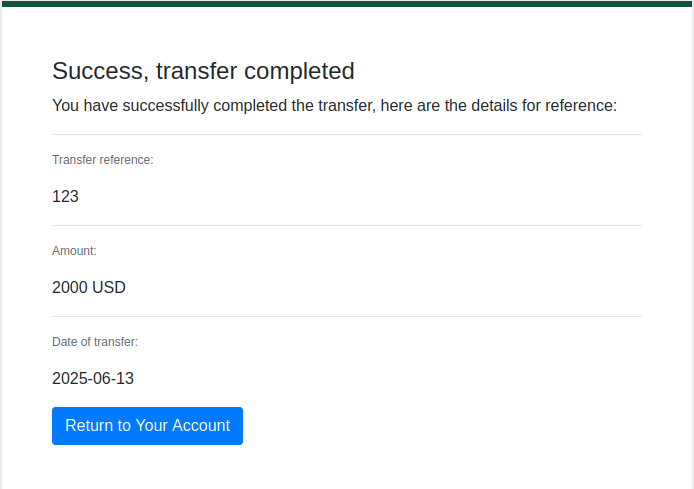
We test by sending a $2000 transfer. The operation succeeds without any form of authentication.
4. Retrieving the Final Flag
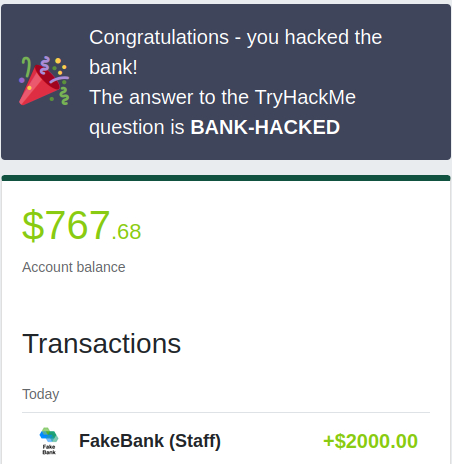
Once we return to the main page of FakeBank, a message appears containing the flag required by TryHackMe to complete the room.
This TryHackMe room is a great example of how simple web enumeration and logical testing can lead to unexpected privilege escalation. By using Gobuster, recognizing sensitive endpoints, and exploiting a poorly protected form, we managed to simulate a bank account takeover.
These small exercises highlight the importance of secure input validation, endpoint protection, and proper authorization checks in web applications.